We want to use AI without risking data privacy, security or client trust
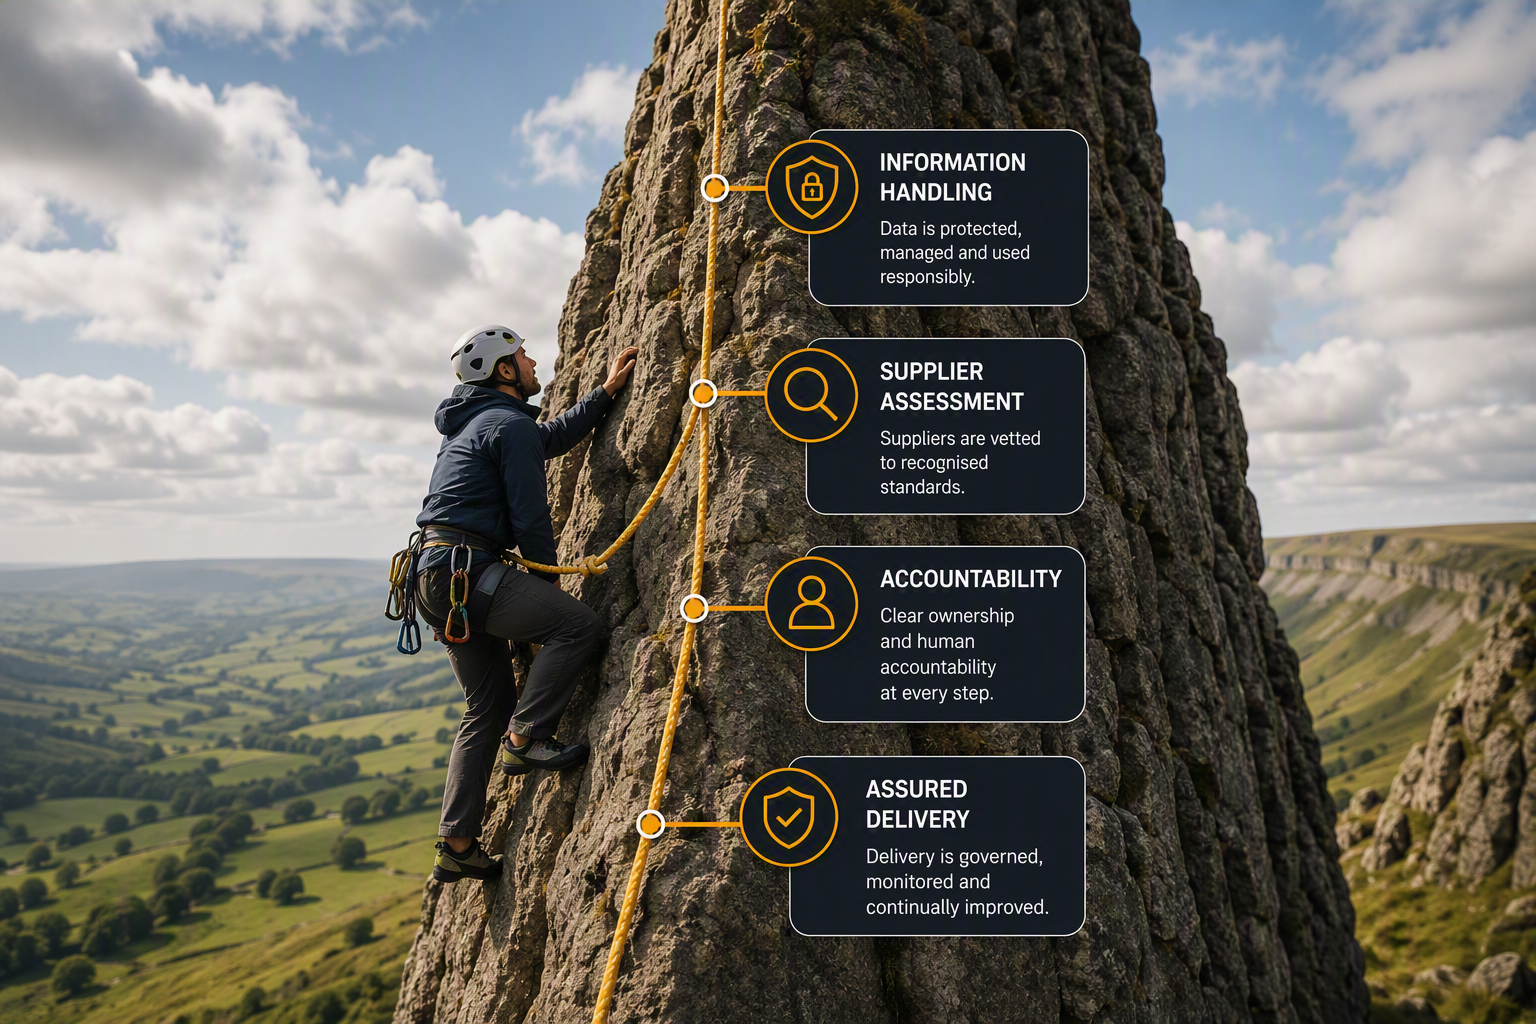
Most organisations want the benefits of AI without putting sensitive information, client confidentiality or regulatory duties at risk. That caution is sensible. The difficulty is that a signed licence, a supplier’s security page or a general reassurance is not enough to earn confidence.
Before AI touches real data, leaders need clear answers on access, storage, processing, retention, supplier use, accuracy and accountability. When those answers are missing, teams either avoid AI altogether or use it quietly without controls. Both outcomes carry risk.
Why data privacy and security concerns stall AI adoption
AI is often introduced as a tool first and a data decision second. A product is chosen, a licence is bought and people are encouraged to try it. The specific questions about information, access and supplier terms are left until later, or assumed to be someone else’s job. That gap is where trust breaks down.
Common concerns include:
- Sensitive client, patient or personal information could be entered into a tool without clear rules.
- No one is certain where the data is stored, processed, or which country it leaves.
- It is unclear whether the supplier uses inputs to train its models.
- Retention and deletion are undefined, so information may persist longer than the organisation intends.
- Access to inputs, outputs and usage records is not controlled or logged.
- Outputs are trusted without a human check, creating a risk of inaccurate or biased decisions.
- Regulatory duties, for example under UK data protection law, are assumed to be met rather than confirmed.
- No single person is accountable for privacy, security, accuracy and the audit trail.
The result is either paralysis or unmanaged risk. Some teams avoid AI and lose ground. Others use it informally, outside any policy, and expose the organisation to the very risks leaders were trying to prevent.
Vague assurances are not a control
“The data is secure” is a claim, not a control. Client confidentiality and regulatory duties depend on how a specific tool is configured, what information it is given, who can see it and what the supplier is contractually allowed to do with the data.
A licence or an enterprise agreement can be a sound starting point, but it does not, by itself, make every use appropriate. Confidence is earned when the organisation can show what information is used, where it goes, who can access it, how long it is kept and who is accountable if something goes wrong.
What safe, trustworthy AI adoption looks like
Trustworthy AI adoption is not measured by how strong a supplier’s security page reads. It is measured by whether the organisation can explain and control how information is handled. A stronger position usually has the following features:
- The information AI needs is defined, and anything unnecessary is excluded or minimised.
- Storage and processing locations are known and acceptable for the data involved.
- Retention and deletion are set deliberately, not left to a default.
- Supplier terms on data use and model training are read, understood and acceptable.
- Access to inputs, outputs and usage records is limited to the right people and logged.
- A person reviews or approves outputs wherever an error could affect a client, employee or important decision.
- Accuracy, bias and unexpected outputs have a defined way of being caught and corrected.
- One owner is accountable for privacy, security, accuracy, the audit trail and escalation.
This is what “human in the loop” means in practice: a person reviews, approves or can change an AI-supported output before it affects a customer, employee, service user or important business decision.
The questions to resolve before AI touches sensitive information:
1. Define what information is genuinely needed
Decide what the tool actually requires to do the job, and exclude or anonymise the rest. The safest data is the data you never share. Start with minimising what is used, not with everything the tool could accept.
2. Confirm access, storage and processing
Establish who can see inputs, outputs and usage records, where the information is stored and where it is processed. Make sure the location and access model are acceptable for the sensitivity of the data involved.
3. Set retention and deletion deliberately
Agree how long information is kept and how it is deleted. Do not rely on a supplier default. Match retention to your own obligations and to what clients and regulators would reasonably expect.
4. Check supplier terms and model training
Read what the supplier is allowed to do with your data, including whether inputs are used to train models. If the terms are not acceptable, the answer may be a different configuration, a different tool or keeping certain data out entirely.
5. Place human review where errors matter
Decide where an output must be checked or approved before it affects a client, employee, service user or significant decision. Put a person in the loop wherever an inaccurate or biased result could cause harm.
6. Name one accountable owner and audit trail
Give a single person clear responsibility for privacy, security, accuracy, escalation and the record of who did what and why. Accountability cannot be delegated to a licence or a supplier.
How AI Terrain helps you adopt AI without compromising trust
AI Terrain helps SMEs, mid-market and third-sector organisations adopt AI in a way they can explain to clients, staff and regulators. We start with the business outcome and the information involved, not with a product.
We map how the work happens now, identify where sensitive data appears, and test each opportunity against value, data, privacy, security, ethics, people and delivery constraints. We work with your existing IT team and suppliers rather than around them.
Depending on what the evidence shows, the next decision may be to:
- reduce or anonymise the information a tool is given
- change how a tool is configured, accessed or logged
- adjust retention, deletion and supplier terms
- add human review at the points where errors would matter
- define ownership, guidance and an audit trail
- choose a more suitable tool, or keep certain data out of AI entirely
A useful outcome is not always more AI. Sometimes it is a clear decision to proceed with defined controls, and sometimes it is a decision not to use AI for a particular task. AI Terrain remains solution-agnostic, so the recommendation follows your business need, your data and your obligations rather than a preferred vendor. Book a one-hour, senior-led transformation advisory session that helps you pressure-test a business, change, technology or transformation decision before committing budget or resource.
Data privacy and trust cannot be delegated to the licence
An approved licence does not automatically make every use appropriate. The controls depend on the use case, the information involved, the supplier terms and the way the tool is configured.
Before client, employee or service-user information is used, the organisation should understand:
- what information is genuinely required and what can be excluded
- who can access the input, output and usage records
- where information is stored and processed
- how long it is retained and how it is deleted
- whether the supplier may use information to train its models
- where human review, approval and escalation are required
- how inaccurate, biased or unexpected outputs will be handled
what audit trail demonstrates who did what and why
These questions do not prevent responsible AI adoption. They are what allows employees, clients and regulators to trust how the tool is used.
AI data privacy and security: the questions leaders ask
Does an approved or enterprise AI licence make our data safe?
Not on its own. A licence sets the commercial and legal starting point, but safety depends on what data you share, how the tool is configured, who can access it and how outputs are checked. The licence is one control among several, not a guarantee.
Can we keep client and personal data out of AI tools entirely?
Often, yes, and it is frequently the right call. Many tasks can run on anonymised, summarised or non-sensitive information only. Minimising what AI ever sees is usually the strongest and simplest control.
Who is accountable if an AI tool mishandles data?
Your organisation remains accountable to clients and regulators for how information is used, even when a supplier provides the tool. That is why a single, named owner for privacy, security, accuracy and the audit trail matters more than any supplier assurance.
Do we need to meet UK data protection duties before using AI?
Your existing duties continue to apply when AI is involved. AI Terrain helps you identify where a use case touches those duties and what controls are needed. This is practical guidance, not legal advice, so confirm specific regulatory positions with your data protection or legal adviser.
The fastest way to a clear starting position is a conversation.
Request a Recce: One hour, free, with a senior advisor and your business on the table. You will leave with an honest view of where you stand, what is worth doing first, and what a sensible next step would cost. No slides, no pitch.